

Digital Security for Remote Workers and Digital Nomads Traveling Abroad

Key Takeaways
The numbers tell a striking story: as of 2024, 18.1 million American workers describe themselves as digital nomads, a staggering 147% growth since 2019, according to the MBO Partners State of Independence Report. Today, one in every ten U.S. workers is nomading in some form, tapping into Wi-Fi networks from cafes in Lisbon, co-working spaces in Bali, or hotel lobbies in Tokyo.
But every airport lounge, hostel hotspot, and foreign SIM card is a potential attack surface. The global average cost of a data breach hit $4.88 million in 2024 (IBM Cost of a Data Breach Report), and 72% of business owners say they're actively worried about cybersecurity risks stemming from hybrid and remote work. For workers crossing borders, those risks multiply dramatically.
Whether you're a seasoned globetrotter or taking your first "workcation," here's what you need to know to keep your data, and your employer's data, safe while working abroad.
The threat landscape: what's actually targeting you
Before jumping to solutions, it's worth understanding the specific threats that make travel so much riskier than working from home.
Public Wi-Fi: a hacker's playground
The hotel lobby, the airport gate, the neighborhood coffee shop, these are the unofficial offices of the digital nomad. They're also prime hunting grounds for cybercriminals.
Man-in-the-Middle (MitM) attacks are among the most common threats on public Wi-Fi networks. A bad actor positions themselves between your device and the router, silently intercepting everything you send or receive: login credentials, emails, work documents, financial data.
Even more insidious is the Evil Twin attack: a hacker sets up a fake Wi-Fi network with a name nearly identical to the real one. "Hotel_Guest" becomes "Hotel-Guest." You connect without a second thought, and everything you do online flows straight to the attacker.
And this isn't just theoretical. Packet-sniffing tools are freely available, and in countries still running older WEP encryption, your traffic can be cracked in minutes.
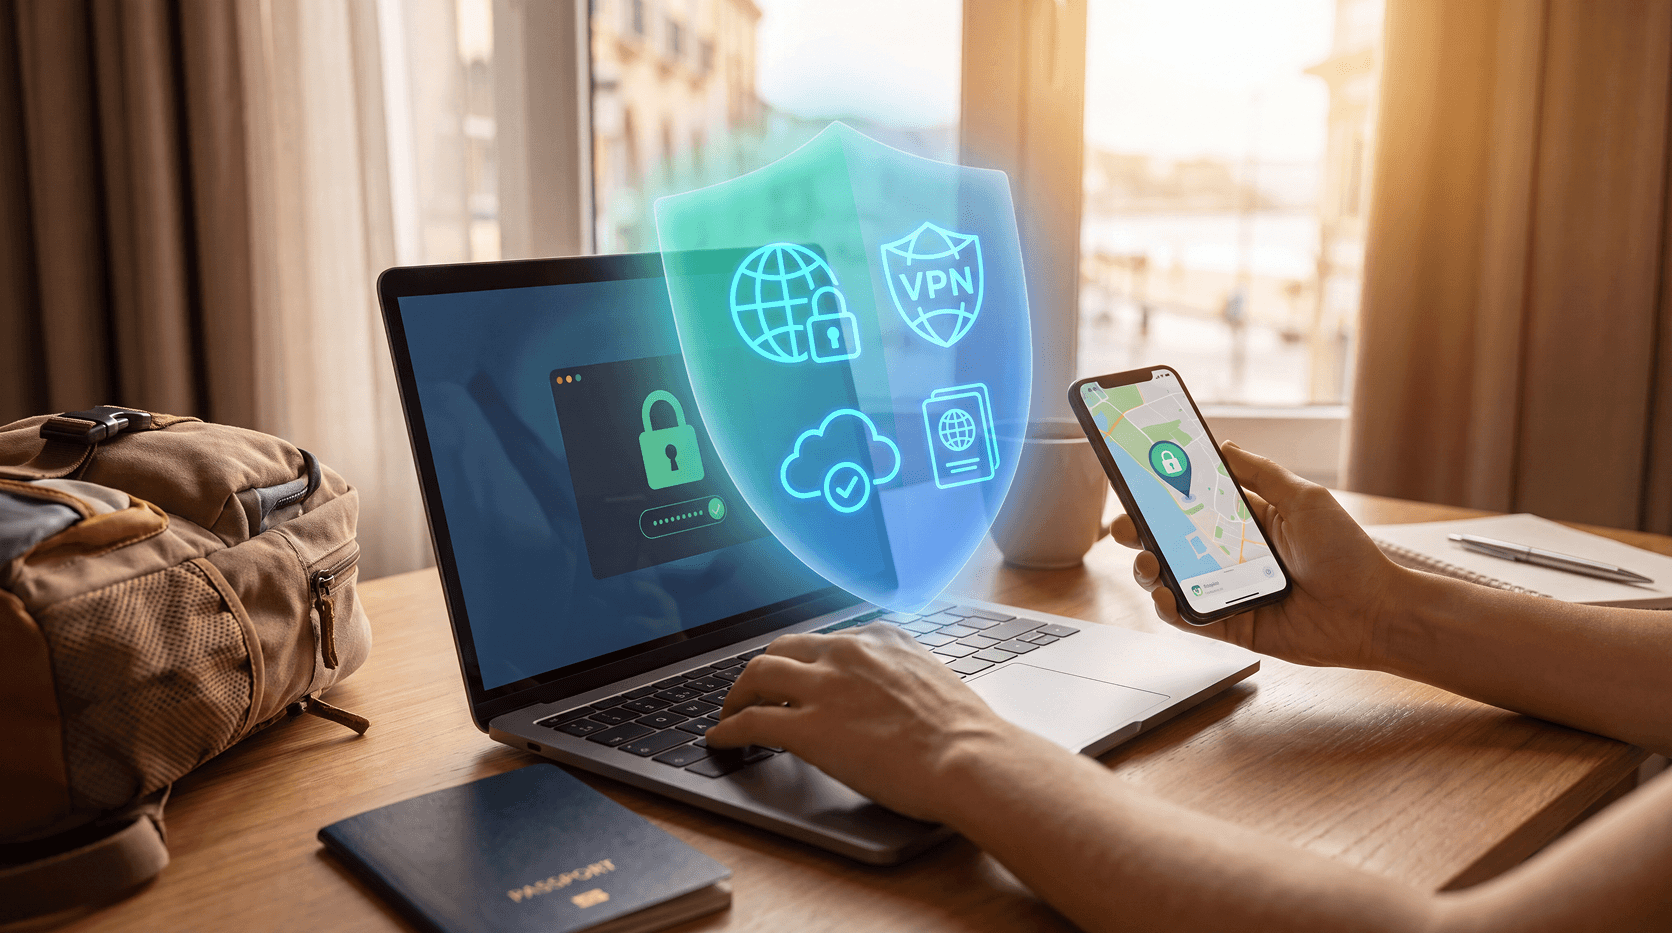
The fix: Never connect to public Wi-Fi without a VPN. A Virtual Private Network encrypts your internet traffic end-to-end, making intercepted data unreadable. Consider it non-negotiable for any travel work setup.
Juice jacking: the USB charging trap
You're low on battery at the airport. You spot a USB charging port built into the seat. It seems harmless. It might not be.
Juice jacking is an attack where cybercriminals tamper with public USB ports to deliver malware to connected devices, or to silently extract data. In 2023, the FBI's Denver field office issued a public warning urging travelers to avoid public USB charging stations due to the risk of malware and data theft, a warning the FCC has also echoed in its consumer guidance.
The USB cable that charges your phone can also transfer data. Modified ports exploit this dual function.
The fix: Carry your own AC wall charger and cable. If you must use a public port, use a USB data blocker (also called a "USB condom"), a roughly $10 dongle that allows power to flow while blocking data transfer entirely.
Device theft and physical security
Laptops get left at café tables. Bags get snatched on transit. A momentary lapse in a busy train station can turn into a full corporate data breach.
Beyond outright theft, shoulder surfing, someone simply looking over your shoulder while you type passwords or view sensitive documents, is low-tech but effective, especially in cramped co-working spaces or economy class cabins.
The fixes:
- Enable full-disk encryption on all devices before you travel. FileVault on Mac and BitLocker on Windows ensure a stolen laptop is just a brick without your password.
- Always lock your screen when you step away, no matter how briefly.
- Use a privacy screen filter, a thin physical filter that blacks out your display from side angles.
- Enable remote wipe capabilities (Apple's Find My, Microsoft Intune, Google's Find My Device) so you can erase your device remotely if it's stolen.
Phishing with a travel twist
Phishing attacks are already the most widespread form of cybercrime. Travelers face uniquely tailored lures: fake airline delay notifications, fraudulent hotel booking confirmations, spoofed "local SIM card activation" pages, or counterfeit customs clearance emails.
These attacks are getting smarter. AI-generated phishing emails are now virtually indistinguishable from legitimate correspondence, and they can be crafted specifically for your location and travel context.
The fix: Treat every unsolicited email or link with heightened suspicion while traveling. Navigate to airline and hotel websites directly by typing the URL in your browser rather than clicking embedded links. If an email asks for credentials or payment, verify it via a separate channel.
SIM swapping and mobile security risks
Many travelers pick up a local SIM card abroad for cheaper data. Convenient, but if that new number is associated with your SMS-based two-factor authentication, a SIM swap attack can let attackers bypass your 2FA and access your accounts.
The fixes:
- Switch from SMS-based 2FA to an authenticator app (Google Authenticator, Authy, or Microsoft Authenticator). These generate codes locally on your device and can't be hijacked by a SIM swap.
- Before traveling, review which accounts use your phone number for account recovery and update them to use email or an authenticator app instead.
Border crossings and government device inspection
This one surprises many travelers: in some countries, including China, Russia, and others with strict surveillance laws, border officials can legally compel you to unlock your device for inspection. Government-mandated monitoring software has been documented in certain high-risk jurisdictions.
The fixes:
- For high-risk destinations, consider traveling with a dedicated "travel device": a laptop or phone wiped of sensitive data and configured with only what's needed for the trip.
- Store critical data in the cloud (encrypted), not on the local device, so a seized device yields nothing of value.
- Consult your company's IT or security team before traveling to countries with known device-search policies.
Your digital nomad security checklist
Before every trip, run through this checklist.
Before you leave
- Enable full-disk encryption on all devices
- Enable remote wipe on all devices
- Back up your data (cloud + local encrypted backup)
- Update all software, OS, and security patches
- Switch SMS-based 2FA to an authenticator app
- Install and test your VPN
- Alert your IT department or employer of your travel dates and locations
- Review which accounts are tied to your phone number
While traveling
- Always activate your VPN before connecting to any public network
- Prefer mobile data or a personal hotspot over public Wi-Fi
- Use only your personal charger or a USB data blocker at public ports
- Lock your screen when stepping away, even briefly
- Use a privacy screen filter in public spaces
- Be extra skeptical of travel-themed phishing emails
- Disable auto-connect to Wi-Fi networks in your device settings
Device and account hygiene
- Use a password manager (1Password, Bitwarden): unique, strong passwords for every account
- Don't use the same password for work and personal accounts
- Log out of sensitive accounts when done, rather than leaving sessions open
The bottom line
None of this requires paranoia, just preparation. A locked screen, an active VPN, an authenticator app instead of SMS codes, and a little extra skepticism toward unexpected emails cover the vast majority of what actually goes wrong on the road.
The destinations change. The habits shouldn't.
Get a free security scan with Guardio today and stay protected from phishing and identity theft.
Conclusion
The freedom of remote work and digital nomadism is real and it's growing, but it comes with a responsibility that too many workers overlook. Cybercriminals actively target travelers because they know that being away from familiar networks and routines makes people more careless.
Most of these risks are entirely preventable with the right habits and tools. A VPN, an authenticator app, full-disk encryption, and a healthy dose of skepticism go a long way toward keeping your work life, and your personal life, safe from wherever in the world you happen to be typing.
FAQs
Is it safe to work remotely from another country?
Working remotely from another country is safe when you take the right precautions. Use a VPN on all public networks, switch from SMS-based two-factor authentication to an authenticator app, and enable full-disk encryption on your devices before you travel. The biggest risks, public Wi-Fi attacks, phishing, and device theft, are all manageable with basic preparation.
What VPN should digital nomads use?
Digital nomads should choose a VPN with strong encryption (AES-256), a no-logs policy, and servers in multiple countries. Popular options trusted by remote workers include NordVPN, ExpressVPN, and Mullvad. The most important thing is to have it active whenever you connect to any network that isn't your own mobile data.
What is juice jacking and how can I avoid it?
Juice jacking is a cyberattack where criminals tamper with public USB charging ports to install malware or steal data from connected devices. The FBI and FCC have both warned travelers about this risk, the FBI's Denver field office issued a notable warning in 2023. To avoid it, carry your own AC wall charger or use a USB data blocker, a small dongle that allows power to pass through while blocking any data transfer.
How do I protect my work data when traveling internationally?
To protect work data while traveling internationally, enable full-disk encryption (FileVault on Mac, BitLocker on Windows), use a VPN on every network, avoid public USB ports, and keep your devices locked when unattended. For high-risk countries, bring a dedicated travel device with only the data you need, and store everything else encrypted in the cloud.
Can border agents search my laptop when I travel abroad?
Yes, in some cases. Border agents in China, Russia, and other countries with strict surveillance laws can legally require you to unlock your device for inspection. In the U.S., citizens can decline, though this may lead to delays or your device being seized for examination. To minimize risk, travel with a dedicated device wiped of sensitive data, store critical files encrypted in the cloud rather than locally, and consult your company's IT team before visiting high-risk destinations.
Is public Wi-Fi safe to use with a VPN?
Using a VPN on public Wi-Fi significantly reduces your risk by encrypting your internet traffic so intercepted data is unreadable. A VPN protects against Man-in-the-Middle attacks and Evil Twin networks. That said, a VPN doesn't protect against malware or phishing, so you still need to stay alert to suspicious links and emails on any network.

 Online Security
Guardio & Trilogy Media: Superheroes of the Cyber World


